
Affordable EDR for Modern, Legacy, and Cloud Systems
Endpoint detection and response (EDR) provides continuous visibility into device and host activity to help organizations detect threats, manage cybersecurity risk, respond to attacks, and support compliance. That visibility is increasingly important as cloud adoption, distributed infrastructure, AI and automated attacks, and expanding attack surfaces change how and where organizations defend their systems.
Servers, workstations, virtual machines, cloud instances, containers, container hosts, legacy systems, and OT endpoints still run applications, process data, and execute the activity defenders need to protect. EDR and host-based security provide visibility into what is running, what is vulnerable, what changed, and what a system is doing.
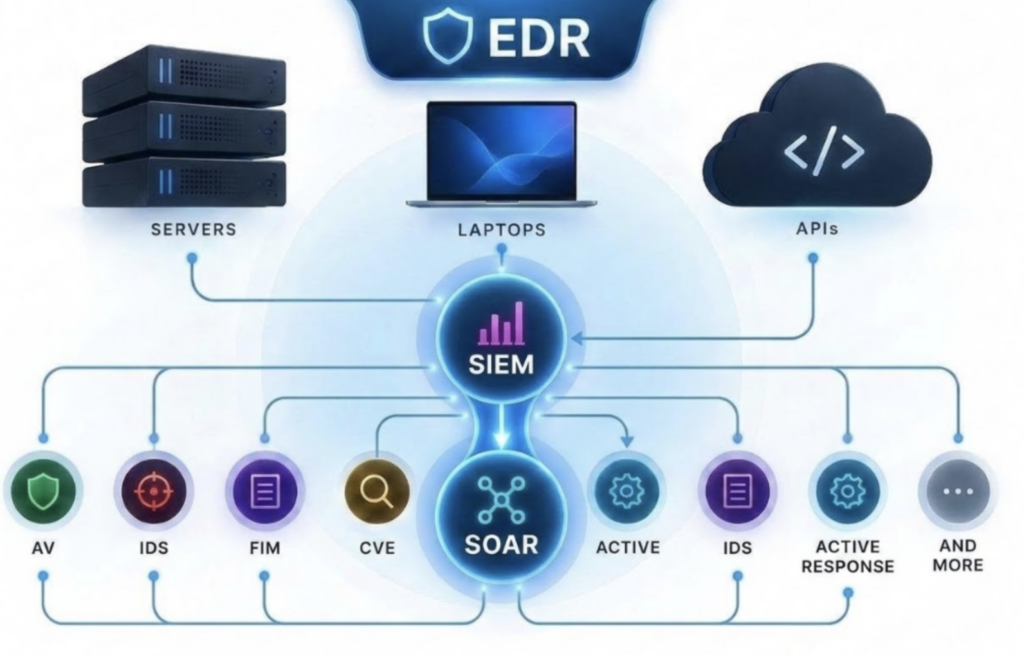
Leading endpoint security systems combine intrusion detection, antivirus and antimalware, CVE and vulnerability detection and management, file integrity monitoring (FIM), and compliance scanning. Since being able to act on detected events is critical, effective EDR must also provide application control, endpoint firewalling, security logging, compliance controls, and automated response.
Discover Atomic OSSEC EDR.
Endpoint Detection and Response Controls for Security and Compliance
EDR can bring multiple security controls and sources of endpoint intelligence together to improve detection, investigation, response, and compliance.
- Endpoint firewall: Controls endpoint network access and communications to support segmentation, least privilege, and containment.
- Application control: Uses application allowlisting and blocklisting to control which applications and processes can run on protected systems.
- Antivirus and antimalware: Identifies and blocks malicious software and suspicious activity that reaches the endpoint.
- File integrity monitoring (FIM): Continuously monitors critical files and systems for unauthorized or unexpected modifications and provides valuable information about what changed.
- CVE detection and vulnerability management: Identifies known vulnerabilities across endpoints so organizations can understand exposure and prioritize remediation. A software bill of materials (SBOM) and CVE correlation can provide deeper visibility into affected software components and associated vulnerabilities.
- Automated and active response: Uses predefined rules and security events to rapidly respond to detected threats, reducing reliance on manual intervention.
- Audit and log controls: Collects and analyzes endpoint security events to support investigations, auditing, reporting, and continuous compliance monitoring.
- SIEM: Centralizes security event information and provides a graphical interface for monitoring, investigation, analysis, and reporting.
- SOAR: Connects security information with orchestration and automated workflows to accelerate threat response.
Check out the Atomic OSSEC EDR.
Agent-Based and Agentless EDR
Agent-based EDR typically provides the deepest endpoint visibility and the most direct detection, security control, and response capabilities because monitoring occurs on the protected system itself. This can provide detailed information about files, processes, vulnerabilities, applications, and other endpoint activity.
But an agent is not appropriate for every system. Legacy and end-of-life systems may have compatibility or resource limitations, while sensitive OT and industrial environments may need to minimize software changes.
Agentless endpoint security provides another approach for monitoring systems where installing an agent is impractical or undesirable. Supporting both approaches allows organizations to apply endpoint security according to the operational requirements of each environment rather than leaving difficult-to-protect systems unmonitored.
Visit the agentless EDR page.
Contact Us about agentless EDR deployments.
EDR for Security and Compliance
EDR is also an important source of the continuous monitoring, vulnerability information, file integrity data, security logs, audit evidence, and response capabilities organizations need for cybersecurity compliance.
These controls can support security programs associated with NIST SP 800-53, NIST SP 800-171, CMMC, ISO/IEC 27001, NERC CIP, 10 CFR 73.54, PCI DSS, and other requirements.
For operational technology (OT) and industrial control system (ICS) environments, host-based and agentless security monitoring can also contribute to programs aligned with NIST SP 800-82, IEC 62443, NERC CIP-010, and related industrial cybersecurity guidance and OT compliance.
Atomic OSSEC EDR: Endpoint Security from Detection Through Response
Atomic OSSEC brings endpoint detection and response, server security, cloud workload protection, and continuous security and compliance monitoring together in one platform. Its capabilities include antivirus and antimalware, intrusion detection, real-time FIM, CVE detection, and vulnerability management. Application control, endpoint firewalling, active response, audit controls, SIEM, SOAR, and extensive security integrations provide additional layers of protection and management
Just as importantly, Atomic OSSEC is designed for diverse environments. Organizations can protect modern and legacy systems across on-premises, cloud, hybrid, air-gapped, and OT environments using agent-based or agentless monitoring as appropriate.
For organizations that need broad endpoint security without the cost and complexity associated with many enterprise EDR platforms, Atomic OSSEC provides an affordable EDR and compliance solution built to protect systems new and old.
Want to learn more about the Atomic OSSEC EDR?

Endpoint Detection and Response (EDR) FAQs
Be a budget hero! Request a 30 minute demo below.
See why thousands of organizations trust Atomicorp for modern, advanced file integrity monitoring and compliance.
