
Compensating Security Controls for When You Can’t Patch
Can’t Patch Old Software Vulnerabilities? Use Compensating Security Controls
Unpatched software systems are an unfortunate reality for many organizations. When vulnerable IT and OT systems can’t be patched, compensating security controls and a defense-in-depth strategy help mitigate the risk while keeping critical systems running.
Why Some IT and OT Systems Can’t Be Patched
Patching known vulnerabilities is one of the most direct ways to reduce cybersecurity risk. But sometimes patching simply isn’t practical or even possible. Legacy software can reach end of life (EOL), leaving no vendor to develop security updates. An organization may also depend on custom software that is too expensive or time-consuming to modify.
Operational technology presents additional challenges. Older or sensitive equipment may not support modern security software, while an update can potentially interfere with the applications or processes that keep industrial equipment running. In its Guide to Operational Technology (OT) Security, SP 800-82 Rev. 3, the National Institute of Standards and Technology (NIST) noted that many OT systems use older operating systems for which patches may no longer be available and recommends compensating controls when patching must be delayed.
Availability can also be the deciding factor. Hospitals, manufacturing plants, utilities, financial systems, and other critical environments may have limited maintenance windows and little tolerance for downtime. Even in general IT environments, NIST recognizes that patching can consume significant resources and reduce system or service availability.
Visit the Atomicorp legacy system security page.
Check out Atomic OSSEC, Atomicorp’s endpoint detection and response system.
The Risk of Unpatchable Software
An old vulnerability does not disappear because the system containing it is old.
Attackers can continue to exploit known vulnerabilities as long as vulnerable software remains accessible. The problem becomes especially important when a vendor no longer supplies a security patch or an organization cannot safely install one.
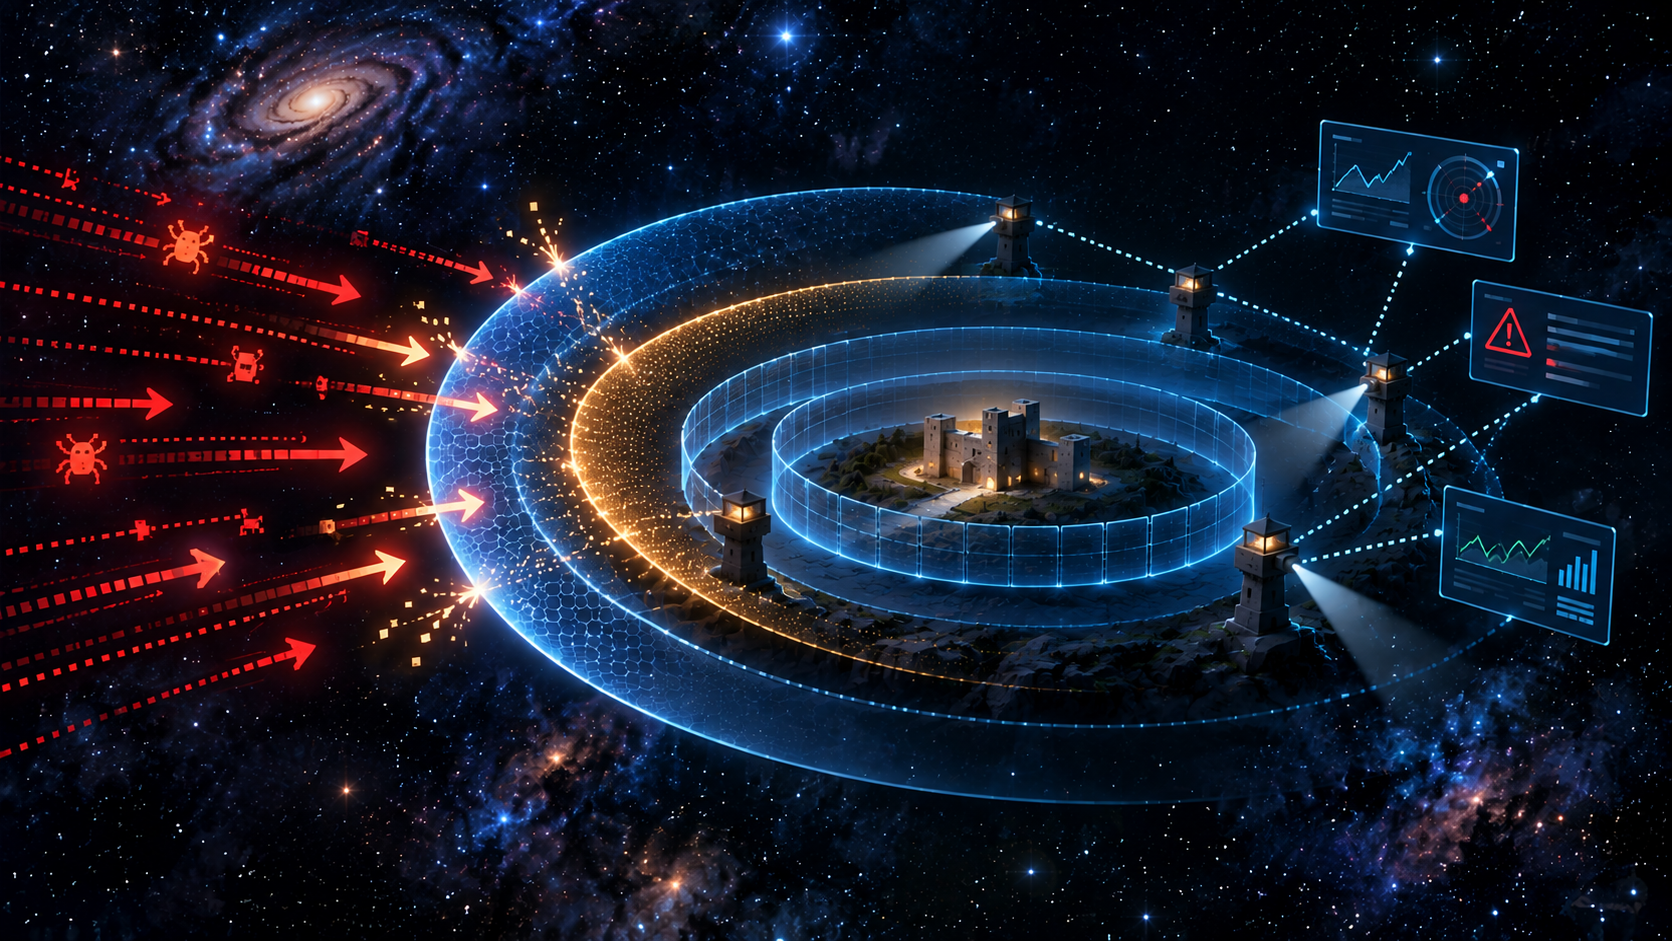
When remediation is unavailable, organizations need another way to reduce exposure. That is where defense in depth and compensating security controls become important. Rather than relying on a single safeguard, organizations can layer Atomicorp compensating security controls around the vulnerable asset and the paths attackers could use to reach it.
Isolate Vulnerable Software
Start by reducing unnecessary access to the vulnerable system. Network segmentation can separate legacy systems from other networks and limit which users, devices, applications, and protocols can communicate with those systems. Firewall rules and other access restrictions can further reduce the attack surface and make lateral movement more difficult.
For particularly sensitive systems, isolation might go further. Traditional air gapping physically or logically separates systems from outside networks. Modern approaches may instead use tightly controlled network zones, gateways, jump hosts, one-way communications, or severely restricted connectivity.
Isolation does not eliminate the vulnerability, but it can remove paths to exploitation.
Shield Vulnerable Assets, Too
Some vulnerable systems can also be protected without changing the underlying software. Virtual patching or vulnerability shielding places a security control between an attacker and a vulnerable application or system. Instead of repairing the vulnerable code itself, the control identifies and blocks malicious traffic or exploit techniques before they reach it.
A web application firewall (WAF), for example, can protect vulnerable web applications from certain application-layer attacks while organizations test or wait for a vendor patch. Broader protections can also address classes of attack or software weakness instead of depending solely on one CVE being defended at a time. MITRE’s CWE system categorizes recurring software weakness types and maps many of them to observed CVEs.
Virtual patching should not be confused with actually patching the software. The vulnerability is still there. The objective is to prevent it from being successfully exploited.
Learn more about Virtual Patching.
Control Applications and Access
Organizations can further reduce risk by controlling what happens on and around vulnerable systems.
Application controls can restrict which software and processes are allowed to execute. Access controls can limit who is authorized to use a system, while endpoint firewalling and network controls can restrict the systems and services with which it communicates. Used together, these controls reduce opportunities for an attacker to turn one exploitable vulnerability into broader access to the environment.
Detect and Monitor What Gets Through
Prevention is only part of defense in depth. Intrusion detection, file integrity monitoring (FIM), log analysis, CVE monitoring, SIEM, and other security technologies can help identify exploitation attempts and suspicious activity. FIM can reveal unauthorized changes to critical files, while centralized security monitoring can correlate events and help teams investigate what happened. Continuous security and compliance monitoring can also help verify that compensating controls remain in place and continue to protect vulnerable systems.
Compensating Security Controls Are Not a Cure-All
Compensating controls mitigate risk; they do not make an underlying vulnerability disappear. Organizations should still patch vulnerable software when a safe, supported patch becomes available and replace obsolete systems when feasible. Compensating controls may also be needed to meet specific formal compliance program requirements. PCI DSS, for example, requires legitimate technical or business constraints and documentation showing how the alternative controls address the original control objective.
The objective is not to make an unpatchable system magically secure. It is to reduce its exposure and make exploitation substantially more difficult while the system remains in service.
Atomicorp Protects When You Simply Can’t Patch
Atomicorp helps organizations build layers of protection around legacy, EOL, and other systems that cannot readily be patched or replaced.
The Atomic OSSEC EDR provides endpoint security capabilities including vulnerability detection, intrusion detection, file integrity monitoring, application control, endpoint firewalling, active response, security monitoring, and other controls. Agentless options can extend monitoring to systems where installing endpoint software is impractical.
For vulnerable web applications, Atomic ModSecurity Rules and Atomic WAF can provide virtual patching and application-layer protection without modifying the underlying application.
Together, these capabilities give organizations practical options for mitigating vulnerabilities when conventional patching is not immediately available—while supporting a broader defense-in-depth and risk management strategy.