Atomic ModSecurity Rules

ModSecurity Downloads, ModSecurity Rules SaaS, and WAFs

Atomic ModSecurity Rules are based on the open-source ModSecurity framework but enhanced for maximum effectiveness and ease of use. Atomic ModSecurity Rules come in three different packages: hosted ModSecurity Rules, ModSecurity downloads, and also a commercial enterprise web application firewall (WAF). 
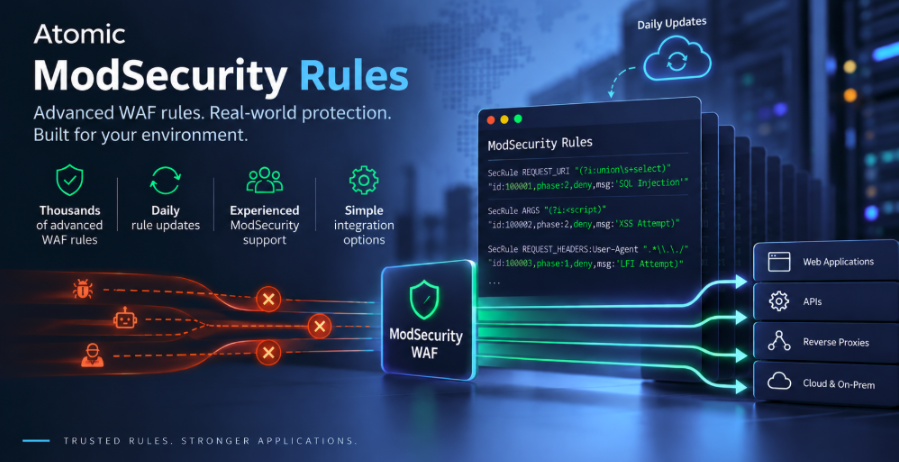
Advanced WAF rules. Real-world protection.

Angled border

Atomic ModSecurity Rules


Get ModSecurity Rules Minus the Management & Maintenance Hassle

This is ModSecurity Rules at its easiest. The monthly ModSecurity subscription option is recommended for IT organizations that don’t want to or can’t develop and manage the rules themselves. Atomic ModSecurity Rules provide thousands of ModSecurity Rules, advanced attack blocking, global threat intelligence, malware protection, virtual patching, and more. It’s advanced commercial ModSecurity rules for organizations that want the familiarity of ModSecurity with less false positives/false negatives, easier implementation and management, and technical support.

Our ModSecurity Rules are maintained and updated automatically, and the customer organization only has to run a one-time installer on its system to be able to employ the rules across web servers and get reports.

Try Atomic ModSecurity Rules Monthly

Get Atomic ModSecurity Rules for $22.50 per server, per month. Volume discounts and bulk licensing options are available. Try one or more licenses risk-free for 14 days. Credit card required; cancel within 14 days.


Angled border

Atomic ModSecurity Integrator


Atomic ModSecurity Rules may also be procured as a downloadable ruleset vs. a hosted offering. Atomic ModSecurity Integrator is our premium ModSecurity Rules download package, all the best ModSecurity Rules we offer plus ModSecurity support.

Atomic ModSecurity Integrator gives customers access to thousands of advanced WAF rules, daily rule updates, and experienced ModSecurity support, with a streamlined way to integrate these capabilities into their own products and services. This makes it easier for MSPs, MSSPs, OEMs, VARs, and providers of reverse proxy solutions such as Varnish to offer advanced ModSecurity protection to their customers.

To inquire about the premium Atomic ModSecurity Rules offer, contact us below.


Angled border

Free ModSecurity Rules


If you need a basic rule set for ModSecurity, Atomicorp offers a free package to help you get started. These rules are not regularly updated or reviewed, but provide baseline rules for using ModSecurity.

We offer paid support and training packages if you need ModSecurity technical support. Contact us about professional support engagements.


Angled border

Atomic WAF


An Enterprise WAF Solution With a GUI and More

Atomic WAF is our enterprise web application firewall, which is continuously enhanced with evolving ModSecurity and Atomicorp cybersecurity rules, false positive and false negative-reduction machine learning logic and professional support. Additional capabilities and features including MFA SSO, Cloudflare integration, a management console and GUI, compliance reports, and more.

Learn more about our enterprise WAF solution, Atomic WAF. Visit the Atomic WAF page.


ModSecurity Rules: Software and Support to Extend and Sharpen Your WAF

Atomic ModSecurity Rules provides the web protection capabilities and expertise for your digital enterprise. It empowers you to:

  • Defend your web applications and APIs against credential theft, code injection, brute-force attacks, SQLi, XSS, CSRF, denial-of-service (DoS) attacks, and other web-based threats.
  • Get or build defense-in-depth (layered) security into your web server and application environment, including Layer 7 protection, especially important in managing multiple customer domains and multiple tenant environments such as Plesk and cPanel and Kubernetes and container environments.
  • Get the security rules needed for DevSecOps. Be able to engineer security into the application, cloud or container environment. Use customizable Atomic ModSecurity Rules to support myriad Web applications such as WordPress, Drupal, Joomla, and many more.
  • Address OWASP Top 10, and use and build rules in accordance with OWASP web application security community principles and designs.
  • Reduce the exposure risk on unsupported web applications through virtual patching

Schedule a demonstration.

ModSecurity FAQs

What is the difference between the OWASP ModSecurity Core Rule Set and Atomic ModSecurity Rules?

The OWASP ModSecurity Core Rule Set (CRS) is a free, open-source set of generic attack detection rules for ModSecurity and compatible web application firewalls. It provides broad protection against common web application attacks, including SQL injection (SQLi), cross-site scripting (XSS), local file inclusion, and other threats represented in the OWASP Top 10. CRS is widely used and provides a strong foundation for organizations that have the expertise to deploy, configure, tune, and maintain their own ModSecurity implementation.

Atomic ModSecurity Rules are a commercially maintained ruleset designed for organizations that need more extensive, continuously updated protection and professional support. The subscription includes thousands of rules, daily updates, advanced web attack blocking, virtual patching, threat intelligence, malware protection, and professional ModSecurity support. Atomicorp also develops protections for specific and emerging threats and provides assistance with false positives and rule-related issues.

Both approaches use ModSecurity to inspect web traffic and block malicious requests. The main difference is that CRS provides a community-supported, general-purpose security baseline, while Atomic ModSecurity Rules add a larger commercially maintained body of rules, frequent threat-driven updates, advanced protections, and professional support for organizations that do not want to develop and maintain that level of protection entirely in-house.

When should enterprises build their own WAF with Atomic ModSecurity Rules, and when should they choose a prebuilt enterprise WAF?

Deploying your own WAF with Atomic ModSecurity Rules can provide greater flexibility, control, and integration options. ModSecurity is versatile and modular, making the option well suited for organizations able to configure and manage their own WAF architecture, integrate protection into existing infrastructure, and tailor deployment and rules to their applications and environment.

A prebuilt enterprise WAF emphasizes convenience and centralized management. It is largely a ready-to-deploy solution with a graphical interface that can make configuration, policy management, visualization, reporting, and compliance activities easier, while making WAF administration accessible to stakeholders beyond security engineers. The choice generally depends on whether an organization places greater value on customization and integration flexibility or streamlined deployment and ongoing management.

Can Atomic ModSecurity Rules protect legacy web applications and vulnerabilities that cannot be patched?

Yes. Atomic ModSecurity Rules and Atomic WAF can be used to help shield vulnerable legacy, end of life (EOL), and unsupported web applications and software from exploitation. Through virtual patching and advanced web attack blocking, WAF rules can detect and block malicious requests targeting known vulnerabilities and attack techniques, providing an additional layer of protection when conventional patching or application upgrades are difficult, disruptive, or no longer available.

Virtual patching does not remove the underlying vulnerability, but it can help mitigate the risk of exploitation. As part of a defense-in-depth security strategy, Atomic ModSecurity Rules and Atomic WAF can help organizations continue protecting applications that must remain in service while they pursue remediation, modernization, replacement, or other longer-term risk-reduction measures.


Read Our Solution Brief for WAF and Web Application Security

Attacks come virtually, across the cloud and internet, putting your communicative web entities at risk. Secure your web servers, websites, endpoints, and data, with Atomicorp zero trust cloud workload protection and ModSecurity WAF.

Read the Atomicorp ModSecurity Rules and WAF solution brief.

Angled border

Request a Demo